The Agency for the Protection of Personal Data (AZOP) has imposed a fine on a casino operator for the unlawful processing of biometric data and non-compliant consent. The total fine amounts to 2,590,000 euros, with the supervisory procedure conducted ex officio against the operator.
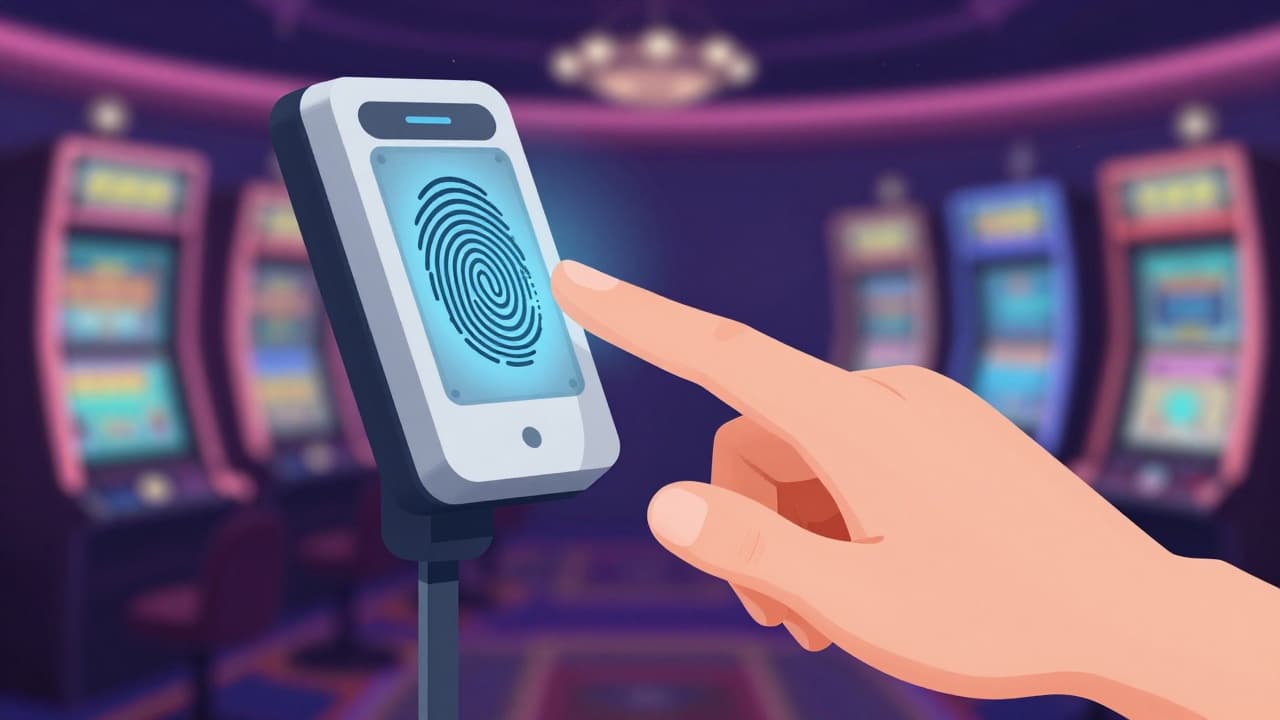
The casino introduced the option of faster identification for returning visitors using an RFID chip or fingerprint, in addition to the standard identification via personal ID. The operator claimed to collect prints from two fingers, but the inspection revealed that biometric identification was being collected for four fingers in total, i.e., two fingers from each hand.
The collection of four finger prints was assessed as processing a greater volume of personal data than necessary. The head of processing stated that the additional prints served as a backup in the event of skin damage to the primary prints, but the supervisory authority rejected this justification, emphasising that the necessity of such processing must be demonstrated concretely.
The inspection confirmed that biometric data was processed without valid consent and beyond the scope necessary for the purpose for a total of 34,933 players. At registration, interactive fields for giving consent were displayed on the screen, but the options for different processing purposes were combined, meaning visitors were not given a genuine opportunity to consent separately to each purpose.
The documents presented contained inconsistent and incomplete information regarding the purposes and legal bases for the processing of personal data. In certain instances, the fingerprint was linked to purposes far exceeding the entry identification, such as access control to business premises, protection of minors, participation in casino games, and loyalty programmes. Players were therefore unable to clearly see for what specific purposes and on what legal basis their data was being processed.
It was concluded that the casino operator had violated the principle of transparency and several articles of the General Data Protection Regulation.